

mongosh or Compass, or from an application then passes through your guardrails, masking rules and audit trail.


Requirements
- An Atlas cluster. This page was tested on the free M0 tier.
- A database user with a password.
- Docker on a host with a static public IP.
- A MongoDB client, such as
mongosh.
Setup
1
Find the primary member
An Atlas connection string starts with The Atlas UI shows the same. Open the cluster, then the Metrics tab. Each member carries 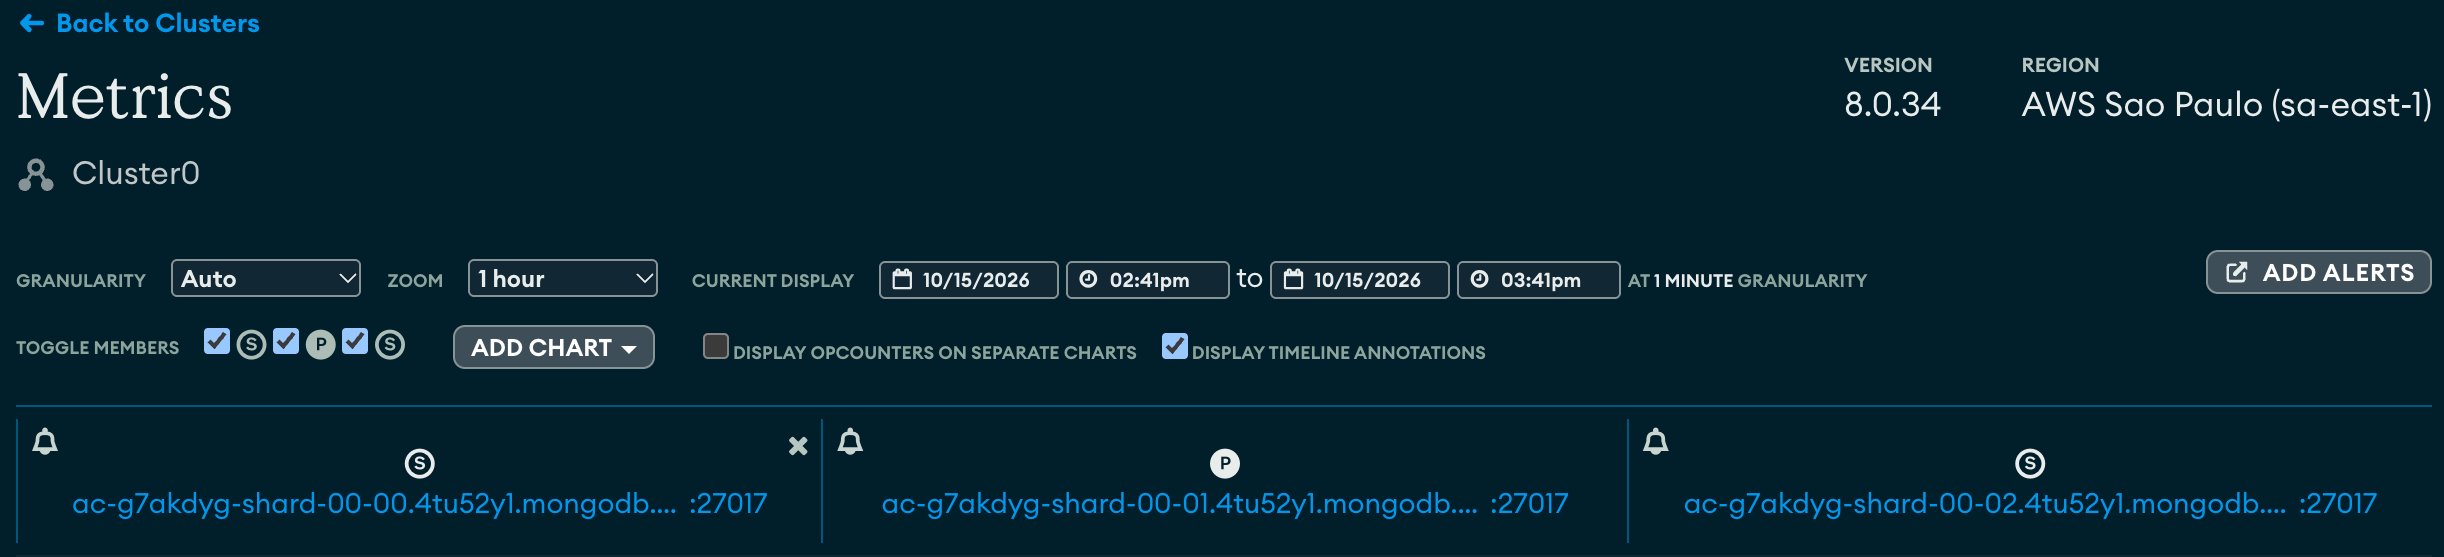
mongodb+srv://. Its host is a DNS record that lists the cluster members, not a server. The Sidecar connects to one member: the primary.Ask the cluster which member is primary:P for primary or S for secondary.The primary changes during failovers and maintenance. See Behavior to know.
2
Write the config
Save this as
config.yaml. Replace the upstream host with your primary.config.yaml
guardrailsblocksdropanddeletecommands.maskreplaces the value of everyemailfield in results, nested fields included.auditwrites every command to stdout as JSON lines, andquery_sessionsturns on the/api/sessionsendpoint.upstream_tlsencrypts the hop to Atlas. Atlas certificates come from a public CA, so the Sidecar verifies them with no extra file.adminserves health checks and the audit API. It has no authentication, so the next step publishes it on loopback only.
3
Validate and start the Sidecar
--validate prints config OK: 1 listener(s) and the rule counts. Versions are on the releases page.4
Point your clients at the Sidecar
Replace the
mongodb+srv:// string with a mongodb:// string to the Sidecar. The user and password stay the same. Every client takes the same string: the MongoDB MCP server an AI agent uses (MDB_MCP_CONNECTION_STRING), mongosh, Compass and application drivers.authSource=adminwas set for you by the+srvstring. Atlas keeps database users inadmin.directConnection=truekeeps the driver on the Sidecar. Without it, the driver reads the member list from the server, dials Atlas directly and fails.- Leave out
compressors=andloadBalanced=. The Sidecar supports neither.
tls=true. That applies only to the hop from the client to the Sidecar on the same host. When clients reach the Sidecar over a network, put TLS in front of it. See TLS on each leg.Verify
Connect through the Sidecar:/api/sessions with no statements, so the example filters on denied=true.
Allow only the Sidecar with the IP access list
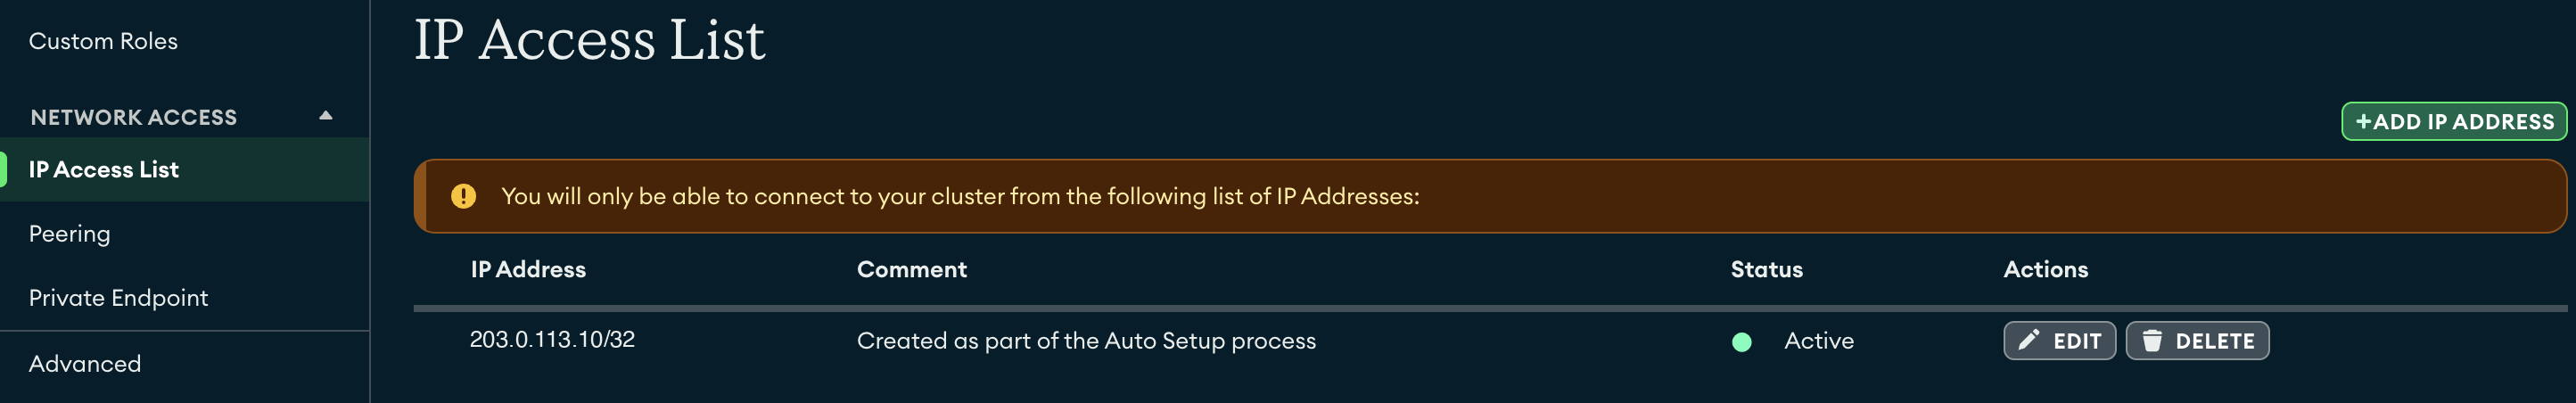
Atlas accepts connections only from the IP addresses on the project’s IP access list. Leave only the Sidecar’s egress IP on it, and no client with another IP can connect to Atlas directly and skip your rules. Workloads that share the Sidecar’s host or NAT gateway keep that access, so give the Sidecar a static egress IP of its own, such as an Elastic IP.- In the Atlas UI, open Security, then Database & Network Access, then IP Access List.
- Click Add IP Address and add the Sidecar’s IP.
- Delete every other entry, including
0.0.0.0/0.
If the Sidecar’s own IP leaves the list, clients see only
connection closed. The Sidecar log names the cause: upstream dial failed with upstream TLS handshake: remote error: tls: internal error.Behavior to know
- A denied command closes the connection. The client reads the rule’s message as error code
13,Unauthorized, and an open transaction rolls back. Drivers retry reads and retryable writes on a new connection. Other commands, such ascreateIndex, can fail once withconnection closed. - A failover leaves the Sidecar on the old member. Atlas elects a new primary during failovers, maintenance and upgrades. Writes then fail with
NotWritablePrimary, and reads come from a secondary, until you setupstreamto the new primary and restart the Sidecar. Rule edits reload live; anupstreamchange needs a restart. - Sessions show
principal: anonymous. The Sidecar relays the login to Atlas and does not read the user name from it, so its audit does not name the database user. Atlas database auditing does, on clusters above the Free and Flex tiers. - This page covers password users. A client’s X.509 certificate does not reach Atlas, because the Sidecar opens its own TLS connection.
Free and Enterprise
Free tier: one Data Masking rule and one Guardrail per Sidecar are free, forever. Running more than one rule per feature, or managing rules centrally across Sidecars, requires Enterprise.
- More rules: an Enterprise license with the guardrails and data-masking features lifts the one-rule caps, with or without a Control Plane. In Docker, pass it with
-e HOOP_LICENSE="$(cat license.json)". See Licensing. - Reviews and central management: connect the Sidecar to a Control Plane, which also needs an Enterprise license. It adds reviews, shared rule sets and one view of many Sidecars.
Next
Guardrails
Write rules that block commands by operation, collection or content.
Data Masking
Choose fields, entity types and masking strategies.
MongoDB
What the MongoDB lane decodes, classifies and masks.
Config File Reference
Every section and field of
config.yaml.